labsecuritywebacademic
Rust Web Software Security
Security coursework with Rust web tooling.- Rust
- Rocket
- PostgreSQL
- OWASP ZAP
This is my Rust software security assignment from my major at the University of Twente. I was
supposed to write a secure web image gallery — and I did. It is a Rocket site backed by
PostgreSQL, brought up with docker-compose, serving image uploads with private galleries.
Scanning it
I set up a clean virtual environment — Ubuntu 22.04 Arm — brought the site up, and checked
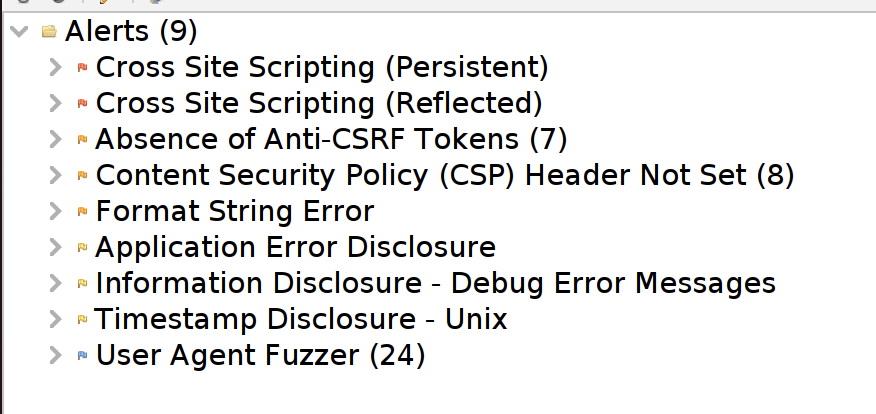
basic functionality first. Then I built OWASP ZAP and ran automated scans against it: the
traditional spider for a first pass, then the AJAX HtmlUnit spider, which took longer and
expectedly found more.
Fixing it
The scans and a read through the code became a hardening pass:
- Proper handling of non-values, with metamacros I prepared for it:
null!,http_code!,define_http!,redir!,templ!. - Transactions and rollback support in
upload_post, so a failed upload cannot leave half-written state behind. - The
xmllintCLI replaced with theminidomlibrary, and theimagemagickCLI with theMagicWandAPI — no shelling out, less room for command injection. - A shield against XSS and an
html_sanitycheck. - SQL injection checks:
tokio_postgresprovides safety in its queries, and'gets escaped in search input. - A
CSPoutlining where images, objects, stylesheets and scripts may come from — seesrc/utils/fairings.rs. - An anti-CSRF solution through the
rocket_csrfcrate, with my modification and work from other open-source contributors — mainlyCsrfForm, which auto-validates the tokens. - UUID-based ids, so private images are harder to predict, plus a unique
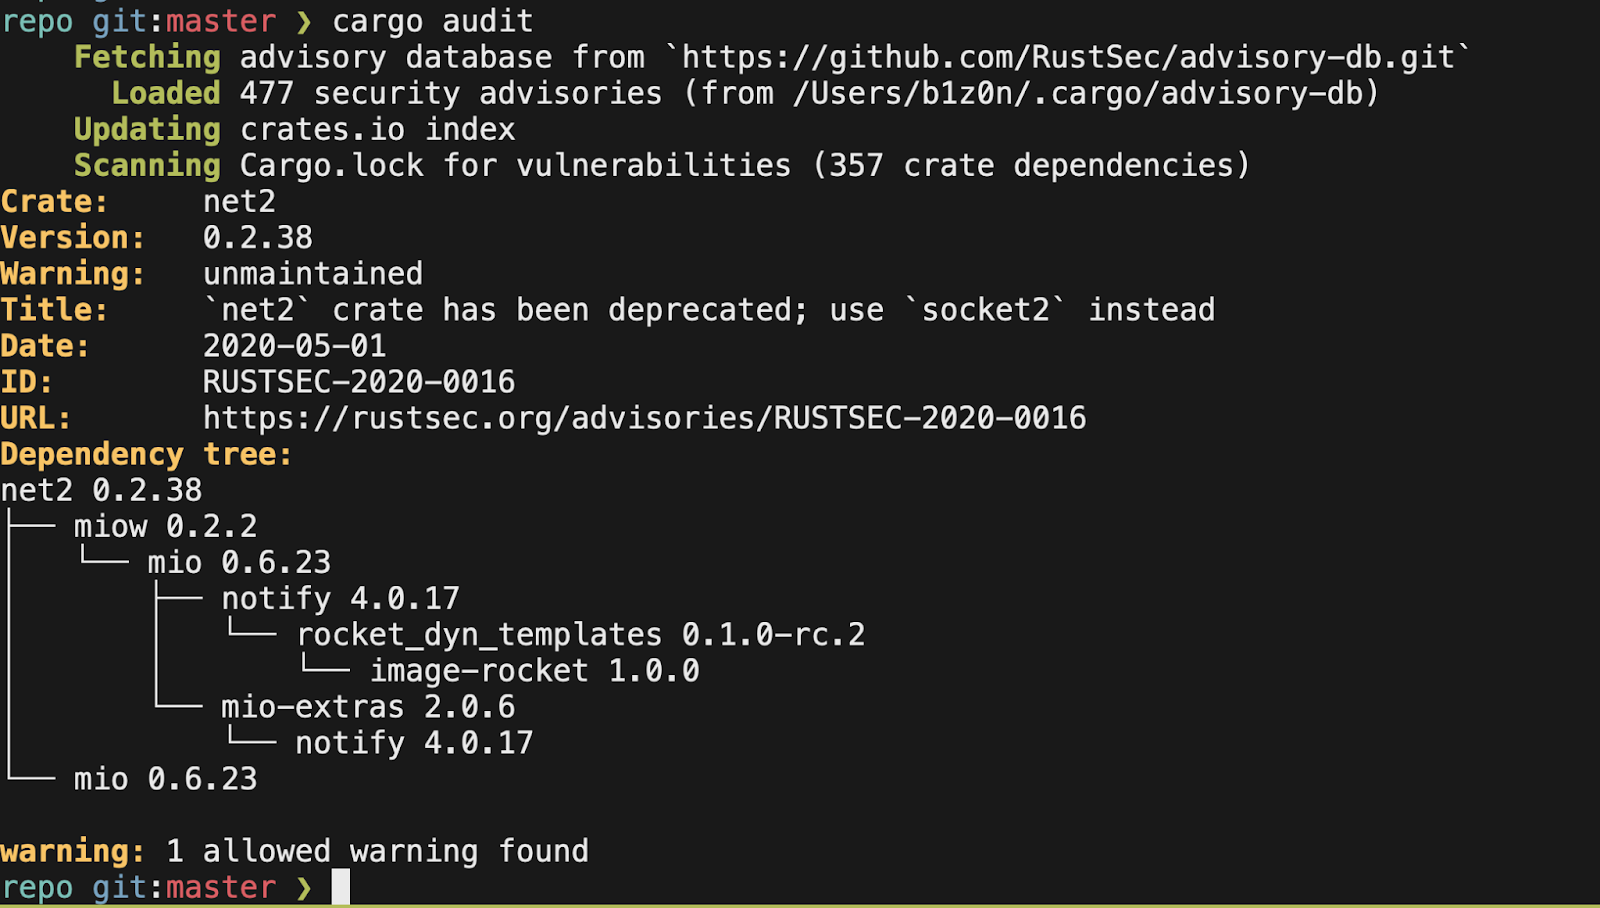
u16in static file naming so nobody can accidentally — or not so accidentally — override someone else’s image. cargo auditover the dependencies, and Google’sosv-scanneron top. Nothing meaningful: a stalenet2advisory on Rocket’s side and a minorattyone.
Along the way I published my own Docker image that builds imagemagick together with Rust on Debian.